Published: October 29, 2026
Category: Cybersecurity / Data Breach
Incident status: Pending verification
Threat actor: ScarlettGroup
A new cybersecurity alert dated October 29, 2026, claims that AU Small Finance Bank, one of India’s financial institutions, may have been targeted by a hacking group known as ScarlettGroup. According to the alert, the group claims to have accessed sensitive customer information and internal corporate records and has threatened to disclose the allegedly compromised data.
The information listed in the alert includes Know Your Customer (KYC) records, PAN and Aadhaar details, bank statements, credit reports, loan applications, insurance documents, employee information, and internal audit logs.
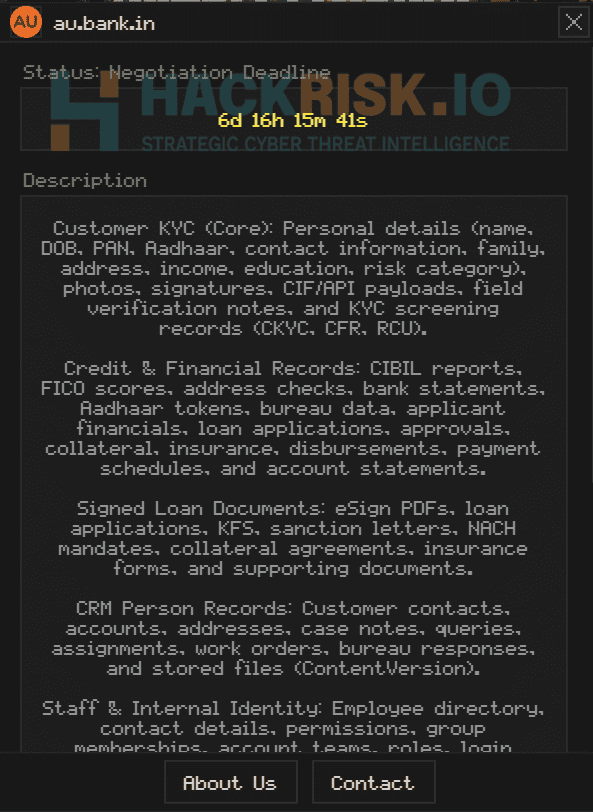
Table of Contents
What Is the AU Small Finance Bank Data Breach Alert About?
The alert alleges that ScarlettGroup gained unauthorised access to data associated with AU Small Finance Bank and threatened to leak sensitive information.
According to the supplied report, the incident involves the financial and insurance sectors. The attackers have reportedly listed several categories of information that they claim to possess.
The key details are:
- Organisation: AU Small Finance Bank
- Threat actor: ScarlettGroup
- Reported date: October 29, 2026
- Alleged incident: Unauthorised access to sensitive data
- Claimed information: Customer identity records, financial documents, loan files, employee data, and internal logs
- Confirmed volume of exposed data: Not specified
- Verification status: Pending verification
At the time of writing, the available information does not establish the number of affected customers, the method of access, or whether the alleged data has been released publicly.
Reference: https://x.com/H4ckmanac/status/2115790335318098295
What Data Does ScarlettGroup Claim to Have Accessed?
The supplied alert lists several types of potentially sensitive information. Each category could create different risks if the claims prove accurate.
1. KYC Records and Identity Documents
Know Your Customer records help financial institutions verify customer identities. The alert claims that the allegedly compromised information may include identity documents and personal identification details, including PAN and Aadhaar information.
If authentic records were exposed, criminals could potentially use them in impersonation attempts, targeted scams, or fraudulent account-related requests.
2. Bank Statements and Credit Reports
Bank statements and credit reports may contain details about financial transactions, account activity, liabilities, and borrowing history.
Such information could help scammers create convincing messages that appear to come from a bank, lender, or financial service provider.
3. Loan Applications and Signed Agreements
The alert also mentions loan applications, signed agreements, and insurance records.
These documents may contain personal, financial, and contractual information. If accessed by unauthorised parties, the information could potentially be used for social engineering, identity misuse, or fraudulent financial applications.
4. CRM and Employee Information
Customer Relationship Management (CRM) records may contain customer contact details, service histories, and communications.
The alert also lists employee information, login histories, and audit logs. If these categories were genuinely compromised, they could raise additional concerns about internal security and the possible misuse of operational information.
Important: These are data categories claimed in the alert, not independently confirmed records of information stolen from AU Small Finance Bank.
Who Is ScarlettGroup?
ScarlettGroup is described in recent cybersecurity reporting as a data-extortion operation that uses alleged data theft and threats of disclosure to pressure organisations. Public threat-intelligence profiles document claims attributed to the group, but an attacker’s listing does not independently prove that a named organisation has suffered a breach. Source: CyberXTron threat analysis.
In a typical data-extortion scenario, attackers claim to have obtained confidential information and threaten to publish or sell it. The threat can create reputational, regulatory, operational, and privacy concerns even when systems have not been encrypted.
For the alleged AU Bank incident, however, the initial access method, evidence of data extraction, and authenticity of the claimed information have not been established by the alert itself.
What Could Be the Impact of a Confirmed Data Breach?
If investigators confirm that sensitive customer or corporate information was accessed, several risks may arise.
Customer privacy risks
Exposed identity documents and financial records could increase the risk of impersonation, targeted phishing, and identity-related fraud.
Financial scams
Criminals may use personal details to make fraudulent calls or messages appear legitimate. For example, a scammer could pretend to be a bank representative and use familiar details to persuade a customer to disclose an OTP or other confidential information.
Corporate security concerns
If employee records, login histories, or internal audit logs were exposed, investigators would need to assess whether the information could assist further unauthorised access.
Regulatory and reputational consequences
A confirmed incident involving personal or financial information could require investigation, appropriate notifications, and other remedial measures depending on the facts and applicable requirements.
These are potential consequences of a confirmed breach, not evidence that any of them has occurred in this case.
What Should AU Bank Customers Do?
While the allegation remains unverified, customers can take sensible precautions without assuming their accounts have been compromised.
- Never share OTPs or PINs. Bank employees should not ask customers to reveal confidential authentication codes.
- Be cautious with suspicious messages. Avoid clicking unexpected links or opening attachments claiming to provide breach updates, refunds, or account verification.
- Monitor bank transactions. Review account activity and report unfamiliar transactions through the bank’s official channels.
- Secure online banking. Use a strong, unique password where applicable, enable available security features, and never reuse credentials across services.
- Verify requests independently. Contact the bank using its official website, application, or verified customer-service number.
- Report suspected fraud promptly. In India, suspected cyber financial fraud can be reported through the National Cyber Crime Reporting Portal at https://cybercrime.gov.in or the cybercrime helpline at 1930.
Customers should not download alleged leaked datasets or share identity documents with unofficial accounts claiming to investigate the incident.
How Can the Alleged Breach Be Verified?
A reliable assessment requires more than an attacker’s claim. Investigators and independent analysts would need to examine evidence and seek authoritative confirmation.
Important verification steps include:
- Checking for an official statement from AU Small Finance Bank.
- Reviewing any relevant notifications from competent cybersecurity or regulatory authorities.
- Establishing whether the alleged records are authentic and genuinely linked to the bank.
- Determining whether unauthorised access occurred and whether information was actually extracted.
- Identifying the affected systems, data categories, and potential number of individuals involved.
Conclusion
The October 29, 2026, cyber alert alleges that ScarlettGroup has breached AU Small Finance Bank and is threatening to disclose sensitive customer and internal corporate information. The categories named in the alert including KYC documents, PAN and Aadhaar details, financial records, loan agreements, and employee information would be significant if the claims were substantiated.
Customers should remain alert to suspicious communications, protect their banking credentials, and monitor transactions. Any further assessment should rely on verified evidence and official updates rather than unconfirmed claims.
Frequently Asked Questions (FAQs)
1. Has AU Small Finance Bank confirmed the data breach?
The supplied alert does not include an official confirmation from AU Small Finance Bank. The alleged incident should therefore be treated as unverified until reliable evidence becomes available.
2. What data does ScarlettGroup allegedly claim to have accessed?
The alert lists KYC records, PAN and Aadhaar details, credit reports, bank statements, loan applications, signed agreements, insurance records, CRM data, employee information, login histories, and audit logs.
3. How many customers are affected?
The alert does not specify a verified number of affected customers or records.
4. Should AU Bank customers change their passwords?
Customers should use strong, unique passwords and enable available security protections as a general precaution. A password change may be appropriate if credentials are suspected of being exposed, reused, or compromised. Customers should follow official bank guidance for incident-specific advice.
5. Could the alleged data breach lead to financial fraud?
If sensitive financial or identity information was genuinely exposed, it could increase the risk of phishing, impersonation, and fraud. However, no resulting fraud has been established by the supplied alert.
6. Where can customers report suspected cyber fraud in India?
Customers can contact their bank through official channels and report suspected cyber financial fraud at https://cybercrime.gov.in or by calling 1930.
7. What is the current status of the AU Bank data breach alert?
As of the alert’s stated date, October 29, 2026, the incident is labelled pending verification. Confirmation of the breach and its scope remains necessary.
Leave a Reply